Encryption
Data is protected in transit and at rest.
Security and trust
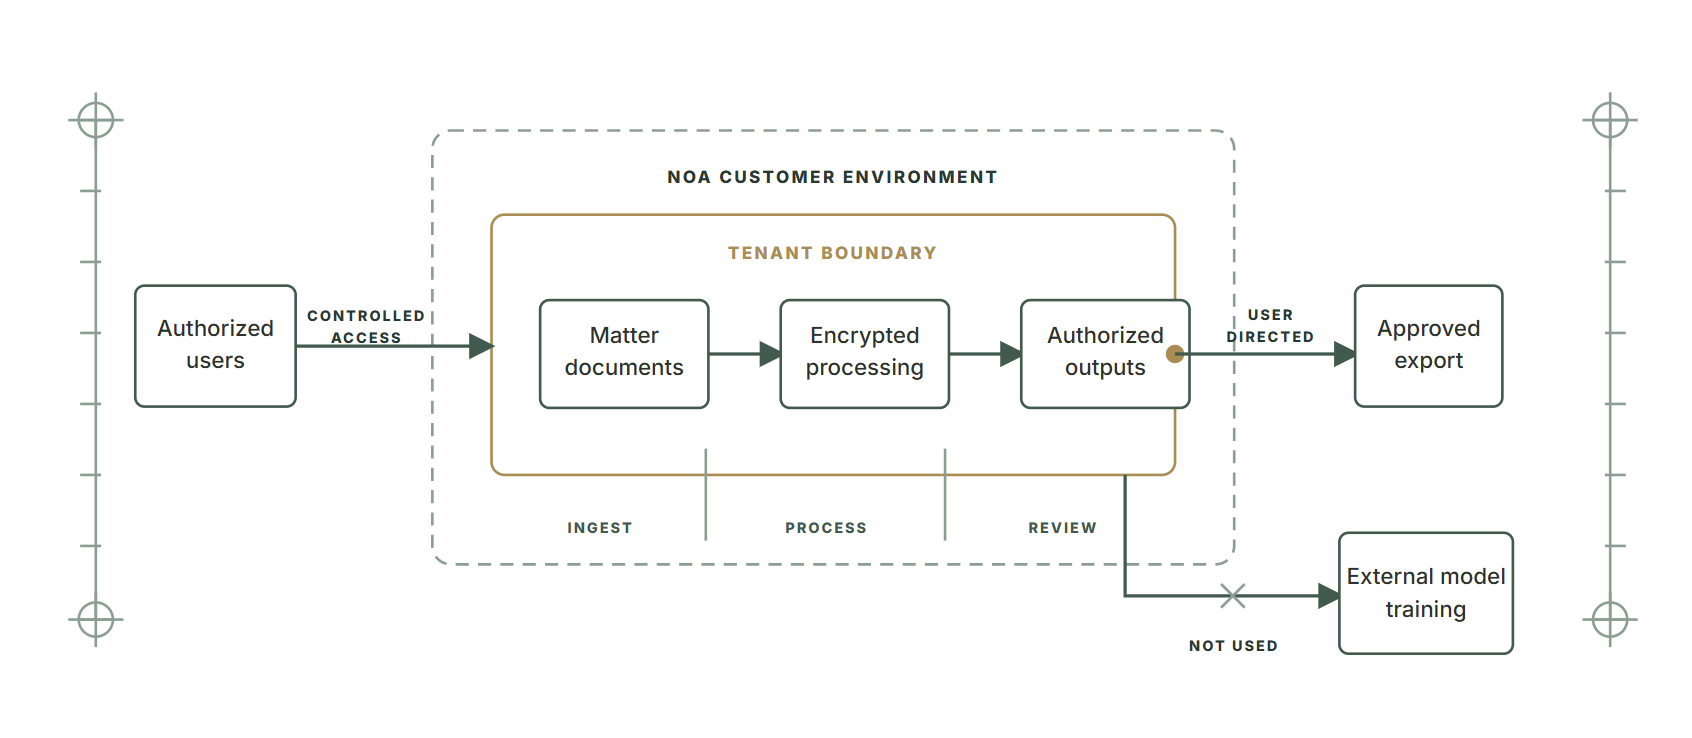
NOA's whole value depends on being trusted with privileged, unpublished, client-confidential material. We designed the data boundary before we designed the product.
Data is protected in transit and at rest.
Customer environments remain logically separated.
Permissions follow organization, role, and matter.
Relevant system activity remains reviewable.
Data boundaries
Security by design
Stored matter content remains protected.
Connections use protected transport.
Access is limited by assigned responsibility.
Organizations remain logically isolated.
Data lifecycle follows configured policy.
Relevant actions can be traced.
Changes follow disciplined review practices.
Defined procedures guide investigation and notice.
FAQ
No. Your data trains a style profile that is available only to your organisation. It never contributes to any model or capability offered to another customer.
Access is governed through role-based authorization, tenant-level separation, and customer-specific entitlements. Users can access only the matters, workspaces, and environments approved for their organization and role.
Yes. Retention policies can be aligned to customer requirements, including configured data lifecycle controls, backup retention, and environment-specific governance needs.
Data is protected through encrypted transport, controlled access paths, and isolated processing environments. Access to customer content is limited by approved permissions and governed throughout the workflow.
Relevant administrative, access, configuration, and application activity can be reviewed to support oversight, security reviews, and customer reporting. Audit scope can be expanded as customer governance needs mature.
Yes. NOA can support customer security reviews with documentation covering architecture, access controls, data protection, operational safeguards, and the boundaries that govern customer information.
Requests for security documentation and completed vendor questionnaires may be directed to us. We respond to all such requests in writing.